Your Metrics Suck! 5 SecOps Metrics That Are Better Than MTTR
summary
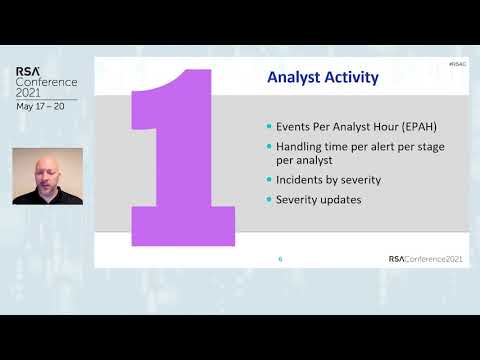
MTTR is the wrong KPI for analysts because it incentivizes speed over correct investigation; replace it with actionable measures like Events Per Analyst per Hour (EPAH), handling time by alert stage, and incidents by severity; track hygiene (unused or duplicate rules, tunes per technology), realized value (percent of device features used — some shops use ~5% — and percent of visible traffic — about 85% is encrypted so without SSL inspection you see ~15%), process deviation and automation failures, and analyst work distribution (30/30/30 split, backup coverage).
AI-written summary · about
chapters (10)
- 0:00Intro
- 0:46Reporting vs Metrics
- 1:45Metrics that matter
- 3:27A personal story
- 9:37Configuration and operational confidence
- 11:42Analyst activity
- 15:46Hygiene
- 20:17Features
- 25:05Process Deviation
- 29:09Analyst Work Distribution
related talks
 42mThe Fault in Our Metrics: Rethinking How We Measure Detection & Response
 01h 00mTop 10 Metrics for Successful DevSecOps Projects
 35mMetrics That Matter: How to Choose Cloud Security KPIs for Your Business
 53mMetrics that Matter.Confidence & Resilience in Your Security Program
 59mDevSecOps Productivity Metrics and Tools
 25mAI Reliability in Security: A New Data Science Paradigm
 53mSecurity Operations 2018: What Is Working? What Is Not.
 34mYour Intrusion Detection Still Sucks (And What to Do About It)