Is Your Organization’s Confidential Data Really Confidential?
summary
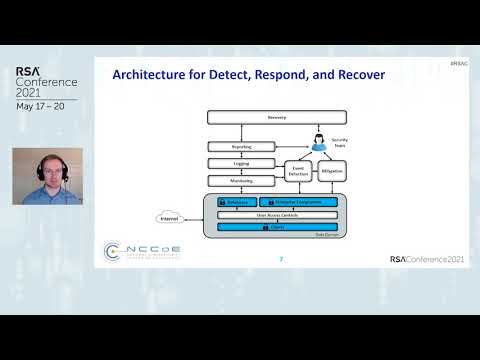
Claims that average breach cost is $3.86M and that two NIST/NCCoE guides (1800-23 ID-PR and 1800-29 DRR) provide deployable architectures and tested builds. Demos show unencrypted continuous exfiltration from a backdoored laptop, ARP‑spoofing capture using arpspoof, and phishing-to-ransomware that steals admin creds. Recommended controls validated in the NCCoE lab include browser isolation, zero trust network protection, strong encryption plus data management, and centralized logging/event detection for mitigation and recovery.
AI-written summary · about
chapters (12)
- 0:00Introduction
- 0:28Data Breaches
- 2:11Data Confidentiality Events
- 6:18NIST Architecture
- 17:44Exfiltration of Data
- 24:15Eavesdropping
- 25:33Demo
- 27:00Network Protection
- 28:25Ransomware
- 32:55Other Use Cases
- 34:25Conclusion
- 35:55Contact Information
related talks
 28mBreaches Are Everywhere; What's a Good Security Leader to Do
 50mThe Price is WRONG - An Analysis of Security Complexity
 46mBreaches Are Everywhere. What’s A Good Security Leader To Do?!
 44mWe (Could Have) Cracked Open the Network for Under $100
 35mPrevention vs. Response - Cybersec Economics in the Modern Era
 01h 00mProtect your assets: A data protection and cyber resiliency panel
 44mCloud Security Essentials
 35mFrom $10 to $30M: Operating in the Data-Extortion Aftermath