Managing Access Entitlements & Their Lifecycle in a Multi-Cloud Environment
summary
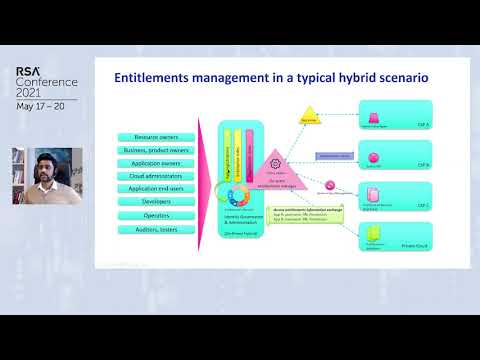
Conference claims that 80–85% of organizations have multi‑cloud and about 50–55% are actively executing; managing entitlements shifts from ad hoc to lifecycle-driven work. Demo uses Azure AD Access Packages to build catalogs, policies, approval flows and automated access reviews that revoke unused guest access. Recommended timeline: 3–4 months discovery, month 3 role design, month 5 role simulation with CSPs, month 8 cross‑cloud deployment, month 10 start role certifications; expect continuous SoD checks and Terraform/scripted deployments.
AI-written summary · about
chapters (11)
- 0:00Introduction
- 0:46Agenda
- 1:53The numbers
- 2:44Key challenges
- 5:07Terminology
- 6:14Cloud Roles
- 10:29Evaluation Criteria
- 23:11Azure Active Directory
- 27:01Access Packages
- 30:33Access Review
- 33:44Summary
related talks
 24mChaos to Control: Automating the Identity Life Cycle in the Cloud
 01h 01mFive best Azure Access Control practice
 18mManaging your cloud security universe as one
 34mScaling access with AWS IAM Identity Center, feat.
 46mHow to Adapt to Security Changes in Cloud SaaS Transformation
 12mIdentity and permissions concerns to watch out for
 51mMeasures for Securing Privileged Users in M365&Azure Every Organization Should Take
 31mA Comprehensive Approach to Cloud Security Posture Management