How to Build a Long-term XDR Architecture Strategy

summary
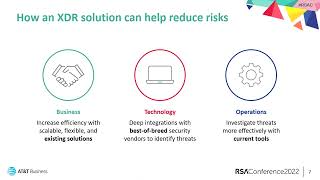
XDR combines endpoint, network and cloud telemetry to cut alert and tool overload by automating detection, investigation and response; recommended foundation is EDR + SIEM foundation feeding correlated telemetry into orchestration and prevention workflows. Expect surprising telemetry: 73% of detections have no reputation record and for certain document types 96% of detected PDFs are previously unknown and deemed malicious. Avoid vendor lock‑in and 70+ tool sprawl, start from business outcomes and key assets, and design for prevention plus orchestrated recovery under 10 minutes.
AI-written summary · about
chapters (12)
- 0:00Introduction
- 1:48What is XDR
- 2:52Expense and Depth
- 3:41The Power of XDR
- 5:55Automated Response and Machine Learning
- 8:49Malicious Activity
- 9:37Ground Up vs Top Down
- 12:20Context
- 14:15Challenges
- 16:45Pitfalls
- 27:34How to Get Started
- 31:24Final Thoughts
related talks
 43mMaking Sense of a Confusing Detection and Response Solutions Landscape
 47mOpen XDR: A Strategy for Evolving Security Needs
 41mCutting Through the Noise of XDR – Are Service Providers an Answer?
 50mWhy Extended Detection and Response (XDR) Must Unite the Industry
 19mDefender XDR in the Real World: Measurable Risk Reduction
 24mThreat Response Needs New Thinking. Don't Ignore This Key Resource.
 46mExtend EDR Visibility by Logging Everything: Demo with Free Integrations
 12mSecurity data gravity: Visibility & threat detection for data lakes