An Analysis of the Role of Situated Learning in Starting a Security Culture in a
summary
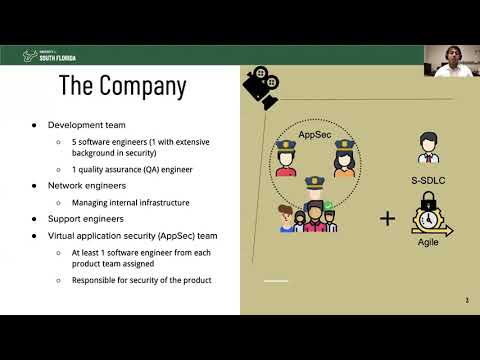
Ethnographic participant observation over eight months inside a five‑engineer agile team shows management mandate plus a co‑located security expert turn security into a deliverable. Concrete practices: creation of a virtual application security team, threat modeling that forces cross‑developer discussion, and security scrum poker to prioritize. Outcome: 20 security tickets filed, 8 included in sprints, visible shifts to threat‑driven design, code refactors, and an emergent cycle of learning where engineers acquire, apply, and contribute security knowledge.
AI-written summary · about
chapters (7)
- 0:00Introduction
- 0:35Methodology
- 1:55Absent Teams Task
- 2:20Threat Model Task
- 3:26Role of Management
- 3:39Data Analysis
- 4:38Conclusion
related talks
 54mScaling Security in Agile Scrum
 57mBuilding a Modern Security Engineering Organization
 24mBeing secure by design: Engineer-led security
 25mWhat Does it Mean to Build a Proactive Security...
 01h 00mImproving the Chances of Success in Secure Software Development
 01h 04mTransformation Blueprint for Developer-Centric Application Security
 27mIncluding security in your engineering culture
 34mSecure by design - the secret weapon of high-performing organisations