Threat modeling state of practice in Dutch organizations
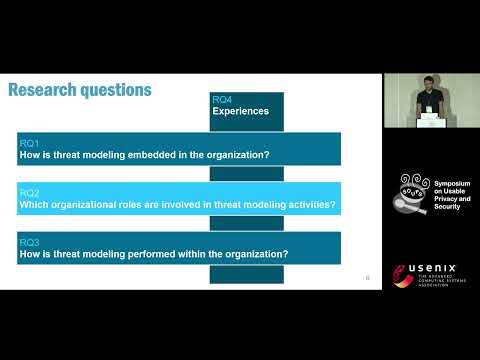
summary
Semi-structured study of 13 interviews across 7 large Dutch organizations finds threat modeling used both to uncover vulnerabilities and—more often—to raise developers’ security awareness; teams prefer intrinsic motivation beats mandates except for critical apps. Sessions use models from whiteboard to DFDs and methods like STRIDE/PASTA/Bowtie, with security teams facilitating developers, product owners and architects. Major practical problems are scoping, missing or stale architectural docs, scheduling and scaling, and weak follow-up and ROI measurement so reports stay deliberately lightweight.
AI-written summary · about
chapters (10)
- 0:00Introduction
- 1:12Research methodology
- 2:35Why organizations perform threat modeling
- 4:21Roles involved
- 6:06Planning and execution
- 7:53System modeling
- 8:58Threat identification
- 9:39Outputs and follow-up
- 10:22Key findings and challenges
- 10:44Future research and conclusion
related talks
 29mRedefining Threat Modeling: Security team goes on vacation
 39mValue driven threat modelling - security by design
 58mThreat Modeling In And For Your Organization
 52mLessons From The Threat Modeling Trenches
 35mValue Driven Threat Modeling
 53mThreat Modeling: uncover vulnerabilities without looking at code
 43mThreat modeling
 50mThreat Modeling With Architectural Risk Patterns