Borderline: Examining the edge cases of FIDO
summary
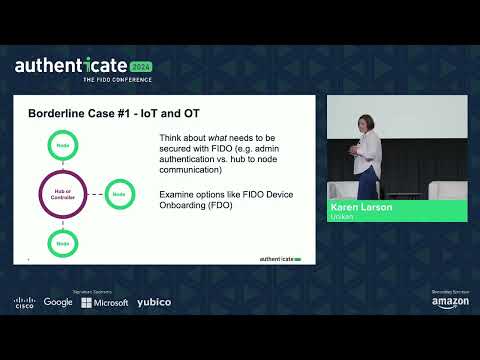
FIDO breaks in three stubborn places: constrained IoT and OT where devices use MQTT hub and spoke networks, lack federation, limited UIs and sometimes require preloaded device credentials at manufacturing which makes FIDO device onboarding the most promising fix; heavy legacy fat clients where backend logins expect user ID and password so common remedies are SSO or adding U2F hooks or using a cross-device sign-in flow; recommend phasing use cases, protect controllers not every system, and combine FIDO with OAuth device flows where needed.
AI-written summary · about
chapters (6)
- 0:00Introduction to FIDO edge cases
- 1:27Why FIDO implementations are hard
- 3:53FIDO for IoT and OT systems
- 12:29Fat clients and legacy apps
- 17:56Kiosk authentication challenges
- 21:29Q&A on FIDO and OAuth
related talks
 02h 22mFIDO 101
 19mTaking FIDO to the masses
 14mSecuring Authentication with and within FIDO
 24mJourney to Implement FIDO
 38mBreaking FIDO: Are Exploits in There?
 23mEnhancing FIDO2 Security for Safety-Critical Applications: Best Practices and Consid...
 21mLeading at the edge: FIDO and the normalization of cryptography
 24mStreaming Authentication