A Shared Services Model to Promote Rapid Adoption of FIDO2 Within Federal Government

summary
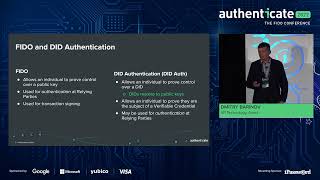
Proposes a concrete architecture that binds derived FIDO2 credentials to existing PIV accounts using a federal trust broker that aggregates agency PIV account status and a DFC marketplace of pre‑vetted ID providers; providers call a common API to check account status before issuing or asserting a DFC and the broker checks a daily push of account state to prevent orphaned credentials. Design is iterated with GSA and NIST over ~18 months, not yet deployed but under active agency discussion.
AI-written summary · about
chapters (10)
- 0:00Introduction and speaker intro
- 2:27Current federal identity landscape
- 7:42Challenges with derived FIDO2 credentials
- 11:32Shared services model concept
- 16:10Establishing the DFC Marketplace
- 18:40Derived credential issuance process
- 20:24Authentication and lifecycle management
- 22:51Advantages of shared services model
- 24:56Call to action and future outlook
- 25:39Q&A: Issuer requirements