Considerations of Leveraging Entra ID Across All Enterprise Applications

summary
OpenText describes using Entra ID and Windows Hello for Business to issue and manage device-tied passkeys, tying biometric or phone-based secrets into conditional access policies that federate into SaaS and legacy apps. Customers report 11 million consumer identities, 25,000 partners, deployments in 180 countries, and typical enterprise estates of 200–300 applications. A healthcare customer refuses a clunky UX, while a booth demo registers ~20 passkeys to show QR-based phone enrollment and seamless SSO into LDAP, RDP and Salesforce.
AI-written summary · about
chapters (8)
- 0:00Introduction and speaker background
- 1:07Enterprise identity challenges
- 3:57Passwordless market adoption
- 6:47Balancing security and user friction
- 10:20Authorization in passwordless systems
- 14:15Reducing business risk with frictionless auth
- 16:41Passwordless beyond phishing resistance
- 17:23Q&A and audience engagement
related talks
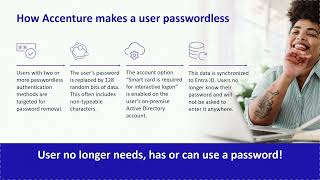 49mGoing Passwordless for Employees: Secure Modern Authentication at Work
 30mWhere we’re going… we won’t need passwords
 11mBuild identity into your apps within minutes!
 22mKeynote, Identity & Authentication in ePromiseland
 47mBuild secure applications with External Identities in Microsoft Entra
 45mSecure your Intelligent Applications with Microsoft Entra
 18mShifting Authentication at Scale
 21mBiometric Authentication, the Zebra way