Timelock Drive: Isolated Time-Based Defense for Storage Systems
Talkat 20th USENIX Symposium on Operating Systems Design and Implementation (OSDI '26) · 2026-07-13..07-15·
summary
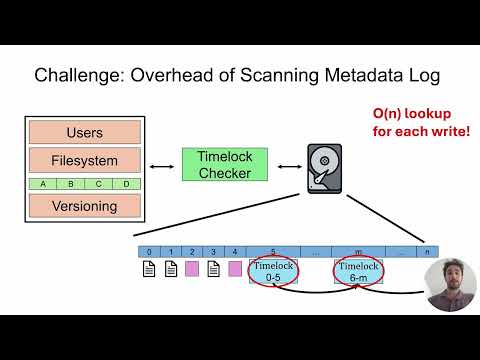
Timelock Drive adds a time lock command to a storage device that makes physical disk blocks immutable for a set duration, forcing attackers to wait. Metadata uses append-only logs with host-cached entries authenticated by freshness counters and hashes, shrinking checker memory from 2 GB -> 1 MB. A small checker in Daphne (≈400 LOC, transpiled to Rust) enforces policies and is formally verified. Recovery requires detection latency shorter than the lock and yields 100% recovery in ransomware VM tests with under 0.5% I/O overhead.
AI-written summary · about
chapters (10)
- 0:00TimeLock Drive intro
- 1:20Time as data integrity defense
- 3:27Isolated time lock interface
- 4:08Secure versioning with time locks
- 7:39Time lock metadata optimizations
- 9:44Recovery with time guarantees
- 11:51Formal verification & ransomware
- 12:57Negligible storage overhead
- 13:39Host-side metadata caching
- 14:01Conclusion & future directions
related talks
 24m🛠 using drand and timelock encryption
 13mMlsDisk: Trusted Block Storage for TEEs Based on Layered Secure Logging
 21mTENET: Memory Safe and Fault Tolerant Persistent Transactional Memory
 14mIs a Ransomware Attack in your Future? How to Prevent an Attack
 38mProtecting Database Backups From Ransomware and Malicious Intent
 34mAuthenticated and Encrypted Storage on Embedded Linux
 22mTowards Temporal Adversarial Logic
 14mProtecting cryptography code from timing vulnerabilities