ORTHRUS: Achieving High Quality of Attribution in Provenance-based Intrusion...
summary
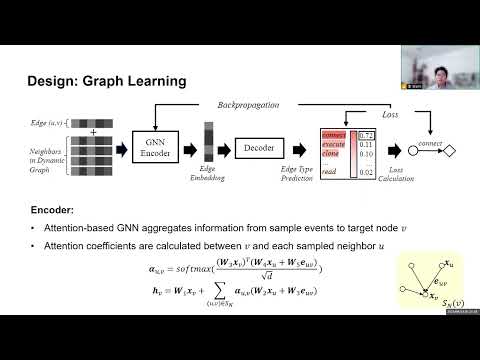
Orthrus is a provenance-graph IDS that pairs a GNN encoder capturing fine-grained spatio‑temporal event patterns with dependency/causality reconstruction to produce node-level attributions. It compares against five state‑of‑the‑art systems, detects all attacks in public benchmarks, and reports the best precision with only a few false positives. The system reconstructs attack paths and reduces nodes requiring manual inspection by several orders of magnitude, improving analyst effort while retaining strong detection and competitive runtime.
AI-written summary · about
related talks
 22mExploring Answer Set Programming for Provenance Graph-Based Cyber Threat Detection: A(…)
 05mConceptualizing attribution and why it matters
 06mUsing Genetic Algorithms for Network Intrusion Detection and Integration into nProbe
 48mHunting Stealth Adversaries with Graphs & AI
 15mLink by Link: Crafting the Attribution Chain
 20mThe Art of Attribution: Identifying and Pursuing your Cyber Adversaries
 39mImproving OT Network and Host Baselines to Secure Critical Infrastructure
 43mOpen Source Intelligence Based Intrusion Detection System