E-Commerce Payment Security Evaluation and Literature Review
summary
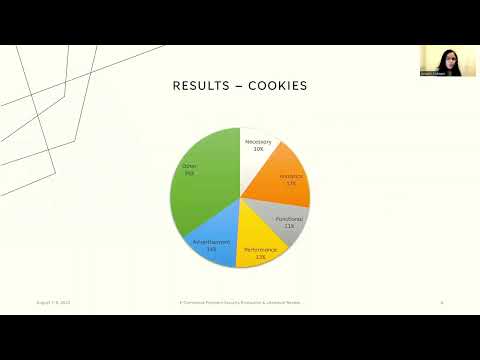
A two-phase study combines a 90-paper review with a hands-on audit of 91 websites analyzed using the Privacy Check browser extension and CookieServe. Findings: most academic work focuses on payment architecture not authentication, cookie categories are mostly "other", only 10% of cookies are necessary and 11% functional, none of the sites document GDPR breach notification, a little more than a third allow guest checkout, over 80% offer address verification secure payment and electronic signature, and all sites validate card details and present a digital certificate.
AI-written summary · about
chapters (6)
- 0:00Start
- 0:14MOTIVATION
- 1:17RESULTS - LITERATURE REVIEW
- 1:29PRIVACY POLICY ANALYSIS
- 3:00RESULTS - PRIVACY POLICY
- 3:31RESULTS - MANUAL ANALYSIS
related talks
 47mCommon security pitfalls in payment apps
 42mSecurity, Fraud, and Compliance Panel
 32mSecurity horror stories in payments
 33mWhere's my dough?! A look at web skimming attacks on
 27mWho Left Open the Cookie Jar? A Comprehensive Evaluation of Third-Party Cookie Policies
 48mRegulation and Risk When Your Customer’s Browser Leaks Data
 17mNavigating Security in the Subscription Economy
 43mReflecting on Twenty Years of Usable Privacy and Security