Account Takeover Attack, It's Detection & Relevance

summary
Workday defends payroll account takeover by combining a rules engine with a machine learning pipeline that runs an XGBoost classifier on access logs. Key inputs are novelty and dossier features — new IP/subnet, city or time of login, browser fingerprint, task-type changes (e.g., bank account edits), and per-user history of anomalous sessions. Detection runs near real time on thin feature slices; rules block known bad IPs while ML scores reduce false positives and prioritize investigations.
AI-written summary · about
chapters (19)
- 0:00Introduction
- 1:00Presentation
- 3:15Payroll Account Takeover
- 5:32Phishing Email
- 6:23How do you identify them
- 7:13Access logs
- 15:23Key takeaways
- 16:35Questions
- 17:22Introductions
- 18:45Presentation Start
- 19:12Presentation Introductions
- 20:00Containers vs VMs
- 21:31Why Kubernetes
- 23:20Where is Kubernetes
- 24:27Digital Enterprise Transformation
- 25:58Case Study
- 27:55Outcomes
- 30:59TLDR
- 33:41QA
related talks
 45mApplying Past Lessons for Intel-Driven Identity Threat Detection
 29mBecoming You: A Glimpse Into Credential Abuse
 31mLog In Through the Front Door: Automating Defense Against...
 12mSpeed, scale & stealth: Securing against ATO events
 26mIntegrating Identity and Fraud
 39mDetecting Website Intrusion and Account Compromise with Machine Learning
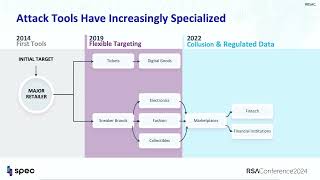 36mAI at the Gates: Combating AI-Driven Assaults on the Customer Experience
 40mWeb Attacks and Fraud: Lessons Learned from the Deep End of the Pool