20/20 Security Vision: Managing Digital Risk in the Era of IoT
summary
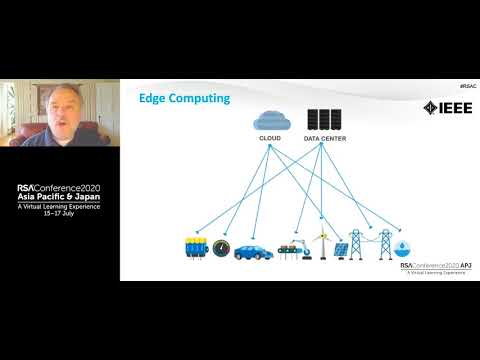
Predicts three times as many devices as people by 2025 and adds 150,000 devices per minute as a concrete growth metric; quantifies IoT-caused DDoS owner costs ($300k from the Krebs botnet, ~$100k from Dyn, up to $68M worst case) and argues for an edge middleware layer to enable local analytics and automated actions (example: shutting down an overheating machine via rules) using open projects like EdgeX Foundry plus agents and services (RSA IoT Security Monitor); urges inventorying devices, adopting NIST IoT baseline, and mapping to standards (MQTT, OPC UA, IIC IISF, FIDO, IEEE, ISO/IEC, IETF) while making IoT part of risk governance.
AI-written summary · about
chapters (19)
- 0:00Intro
- 1:45IoT Market Metrics
- 2:35IoT Risks
- 4:00Digital Transformation Risks
- 7:12IT Evolutions
- 8:50Edge Computing
- 11:10IoT Architecture
- 12:40EdgeX Foundry
- 17:40Standards Frameworks
- 18:55NIST
- 19:55MQTT
- 20:45OPC UA
- 21:35IoT Edge Platform
- 22:52IoT Security Framework IIIA
- 23:52FIDO
- 24:48NC DDS
- 26:27RFC
- 27:40Recommendations
- 29:35Questions to consider
related talks
 27mThe IoT storm... Will we survive the coming deluge?
 28mIoT Security - it's not just the devices
 47mTrend Micro's VP of security research reveals the latest IoT threats and how to combat them
 25mSecuring the Internet of Things - An analyst's view on the market
 51mOptimizing the future: The 5G & IoT revolution
 29mSecuring IoT/OT Against Modern Threats
 53mCXO Panel: OT & IoT Risk Management Strategy For CISOs
 01h 03mPolicy implications of the internet of things