Breaking Bad (Passwords)
summary
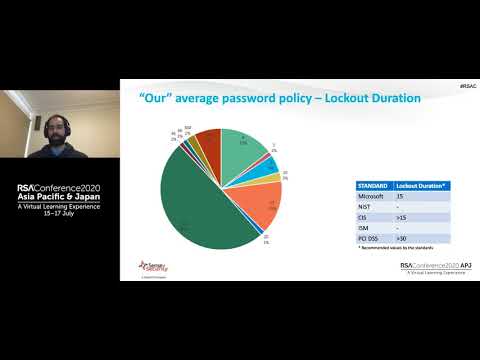
Sense of Security analyzes three years of Active Directory dumps, cracking hashes on a consumer PC with four GPUs in 2–5 hours and finding ~60–73% of passwords at 7–9 characters; 41% of orgs enforce an 8‑char minimum, 43% align to Microsoft/NIST, 1% to CIS, 46% keep 24 password history, and 24% have no lockout. Common hits are Welcome1, Password1 and Company2020 patterns (first capital + trailing digit ~44%). Recommendations: block breached/password‑list words, apply MFA everywhere, use password managers, monitor and audit identities.
AI-written summary · about
chapters (14)
- 0:00Intro
- 0:48Another talk on passwords?
- 4:40Industry guidelines and standards
- 8:40"Our" average password policy - Min Chars
- 10:09"Our" average password policy - Password History
- 10:31"Our" average password policy - Lockout Duration
- 11:15"Our" average password policy - Lockout Threshol
- 12:07"Our" average password policy - Complexity
- 12:22"Our" average password policy - Max Age (Expiry)
- 13:03Who does it better? (on paper)
- 15:14What do the bad guys think of this?
- 21:41Does size length really matter?
- 24:37Some common mistakes and blind spots
- 26:44Some practical advice
related talks
 23mFantastic Passwords and Where to Find Them
 47mYour Password Complexity Requirements are Worthless
 40mLive autopsy of a password: lessons learnt cracking secrets
 25mEverything You Know About Passwords Is Wrong
 46mRequiem for the Password
 23mImplementing "password never expires"
 40mFantastic Passwords and Where to Find Them
 31m680,000 Plaintext Passwords: An Open Source Love Story in Three Acts