Continuous Security by Design
summary
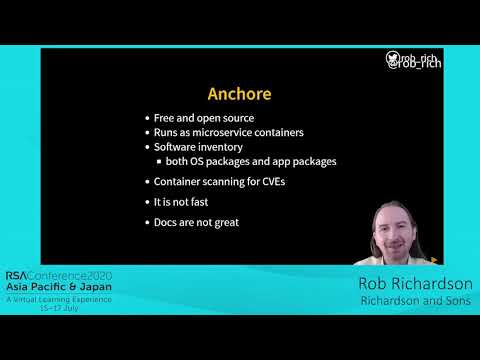
Argument: Kubernetes does scheduling, not runtime isolation, so secure the image. Walkthrough shows adding Anchore (free, microservices) into the build: pip-install CLI, add image, wait for feeds (docs say ~10 minutes but initial sync can take ~1 week), scan OS packages and libraries (it checks packages not arbitrary files), then apply a policy to fail the build. Scanning can run in build, registry, or via Kubernetes webhook to block pods, and can run in GitHub Actions to automate and store reports for continuous rechecks.
AI-written summary · about
chapters (6)
related talks
 46mA Security State of Mind: Continuous Security with Kubernetes
 41mKubernetes Security Jumpstart
 43m6 Strategies to Bring Order to Kubernetes Security Disruptions
 18mContinuous Security - Building Security into your Pipelines
 37mAchieving High Security at Scale with Microservices
 38mTutorial: Building Security into Kubernetes Deployment Pipelines
 33mKubernetes Security Jumpstart
 37mSupply Chain Security in Kubernetes