Keeping Your Software Supply Chain Healthy

summary
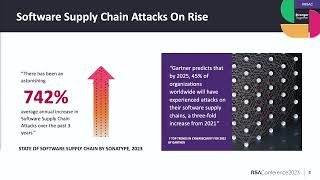
Software supply chains show concrete risks and fixes: attacks doubled in 2024 and there’s a 1300% rise 2020–2023 in malicious packages, average breach cost is ~$5M, and some packages (Next.js) pull in 652 transitive deps. Use SCA, SAST/DAST, SBOMs (SPDX/CycloneDX), scanners like Snyk/Fossa/Whitesource, deps.dev and libraries.io, container scanning, and CI gates. Expect AI hazards (40–60% orgs approve tools yet ~90% of devs use them), prompt‑injection and model backdoors; start with a 90‑day audit, monitoring and dependency cleanup.
AI-written summary · about
chapters (9)
- 0:00Introduction
- 3:09Why software supply chain security matters
- 7:42Poor digital health symptoms
- 13:39Measuring supply chain health
- 22:27AI risks and vulnerabilities
- 28:08Dependency management
- 33:49Organizational best practices
- 39:25Long-term wellness strategies
- 42:1990-day action plan
related talks
 41mManaging the Risk of Software Supply Chain Attacks
 37mSupply Chain Attacks and the Future of Software Delivery
 51mOSS Supply Chain Threats and Why You Need a Holistic Security Strategy
 25mYour Software Supply Chain is Only as Secure as its Weakest Link
 49mMitigate Risks In Code: Protect Your Software based Supply Chain
 49mScaling Software Supply Chain Source Security in Large Enterprises
- 25mYour Software Supply Chain is Only as Secure as its Weakest Link
 39mSoftware Supply Chain Security