The Secret Life of Maven Central

Talkat JCON Europe 2023 · on Thursday, 2023-06-22· at 11:00· Cinema 9, Im Mediapark 1, 50670 Köln, Germany·
summary
Maven Central runs on Sonatype’s Nexus backend, serves ~9 million component versions and handled ~496 billion requests in 2021, costing millions a year on AWS; Sonatype scans every upload and blocks only malware because publishers must prove domain ownership, which largely prevents typosquatting. New features add vulnerability metadata, Sigstore signing, SBOM support and BOM Doctor visualizations; Firewall, Lifecycle and Lift automate scanning in CI/IDE and the Log4j fallout shows ~51 million downloads of a vulnerable version and why shift-left supply‑chain security matters.
AI-written summary · about
chapters (26)
- 0:00Intro
- 1:03About Jamie
- 2:05Hands Up
- 4:02Open Source Dependencies
- 5:23Outline
- 5:56Maven Central
- 8:11Security
- 9:14Origins
- 9:43Highlevel architecture
- 11:32API
- 14:26Marketing
- 14:48Keeping our application safe
- 15:45Vulnerability management
- 22:32Security is hard
- 24:08Vulnerability detection
- 26:24The scary part
- 29:34The problem
- 36:16The bad guys
- 37:34Dependency squatting
- 39:16Sbomb support
- 42:11Bombdoctor
- 42:56Eight Rules
- 44:06State of the Software Supply Chain
- 45:10Homework
- 46:30All Day DevOps
- 47:08Bomb Doctor
related talks
 20mThe Secret Life of Maven Central
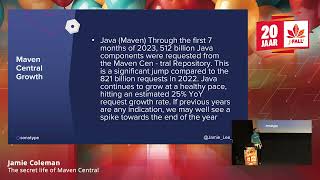 38mThe secret life of Maven Central
 29mThe Secret Life of Maven central
 33mThe Secret Life of Maven Central
 31mOpen Source Supply Chain Threat Landscape - A Moving Target
 48mAn Introduction to the Newest Addition to the OWASP Top 10
 41mSponsored Session: Software Supply Chain Threat Landscapes: A Moving Target
 37mIt’s Not Open Source, It’s You. Where Open Source Risk Comes From