The secret life of Maven Central
summary
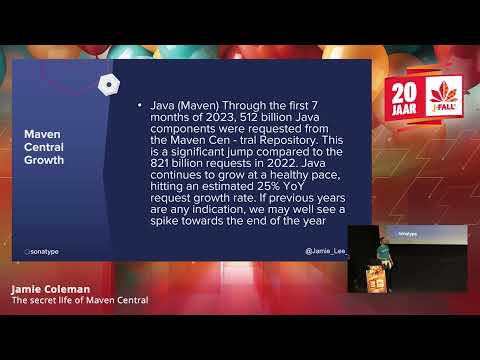
Sonatype runs Maven Central on AWS as a public service, storing ~8.8 million components (27 TB) and serving 2.5 trillion downloads to date; it enforces proof of ownership for publishers and scans every upload with industrial scanners. The service blocks nearly all malware, found 245,000 vulnerable packages last year, and still sees 285 million downloads of a vulnerable Log4j release; recommended practices include an internal repo, firewall between external and internal, and automated lifecycle tooling.
AI-written summary · about
chapters (7)
- 0:00Introduction and speaker background
- 3:49What is Maven Central
- 10:15Maven Central security features
- 16:14Rising cybercrime and supply chain risks
- 21:52Evolving Maven Central for developers
- 25:43Crowdsourcing Maven Central logo
- 26:24Q&A session
related talks
 20mThe Secret Life of Maven Central
 53mThe Secret Life of Maven Central
 29mThe Secret Life of Maven central
 33mThe Secret Life of Maven Central
 31mOpen Source Supply Chain Threat Landscape - A Moving Target
 48mAn Introduction to the Newest Addition to the OWASP Top 10
 37mIt’s Not Open Source, It’s You. Where Open Source Risk Comes From
 45mOWASP A9: A Year Later - Are you still using components with known vulnerabilities?