Lock It and Still Lose It —on the (In)Security of Automotive Remote Keyless
summary
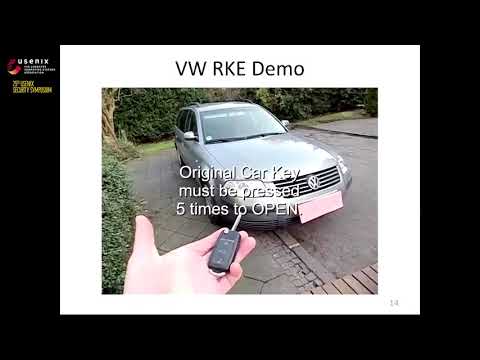
Finds global failures in remote keyless entry: VW schemes (VW1–VW4) use global master key or poor diversification discovered by extracting ECU firmware and reversing with IDA Pro, letting an attacker clone remotes after a single eavesdropped signal so owners must press the fob about five times to resync. Builds a $40 Arduino receiver and uses SDRs; another line breaks Hitag2 with a correlation attack needing 4–8 traces and recovers the 48‑bit key in ~1 minute laptop recovery, then programs an emulator to open cars. Responsible disclosure to VW and NXP.
AI-written summary · about
chapters (21)
- 0:00Intro
- 1:41History of RKE: Fix Codes
- 2:15History of RKE: Rolling Codes
- 3:36Previous Attacks on RKE
- 5:54VW Group RKE: Analysis
- 7:08Example: VW-3
- 8:44Example: VW-4
- 9:21VW RKE Demo
- 10:28Affected Vehicles
- 11:06Intermezzo
- 11:56Hitag2 Usage in RKE
- 12:22Our previous work on Hitag2
- 13:16In the RKE context
- 14:38RKE Protocol (simplified)
- 15:09Our RKE attack requires
- 16:28Hitag2 Cipher
- 17:02A fast correlation attack on Hitag2 (simplified)
- 18:40Practical limitations
- 20:41Hitag2 RKE Attack Demo
- 21:49Vehicles we tested using Hitag2 RKE
- 22:18Conclusions
related talks
 41mThe (In)Security of Automotive Remote Keyless Entry Systems...
 15mSoK: Stealing Cars Since Remote Keyless Entry Introduction and How to Defend...
 44mBreaking the Security of Physical Devices
 41mGrand Theft House: RF Lock Pick Tool to Unlock Smart Door Lock
 37mAutomatic Automotive Hacking
 44mMy Car, My Keys: Obtaining CAN Bus SecOC Signing Keys
 44mResearch Only? Understanding the Scope of Automotive...
 41mPanel: Tackling Automotive Hardware Vulnerabilities