The (In)Security of Automotive Remote Keyless Entry Systems...
summary
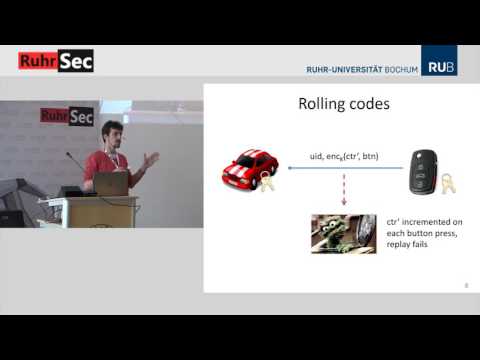
Analyzes automotive RKE systems and shows two concrete, working attacks: extracts a handful of global VW group keys from ECU firmware enabling cloning a remote and unlocking a car from up to 100 m using a single rolling code, and a new cryptanalytic attack on Hitag2 that recovers full keys with 4–8 rolling codes and negligible computation (optimized attack runs in about one minute on a laptop); implements SDR/Arduino sniffers and emulators, validates across many models, and reports coordinated disclosure (VW MQB variants patched).
AI-written summary · about
chapters (15)
- 0:00Introduction
- 0:52Security functions
- 2:58How does it work
- 4:45Cryptography
- 8:02Key Lock
- 14:49Security
- 16:32Analysis
- 20:40VW3 system
- 23:14Demonstration
- 26:24Contributions
- 30:19HighTech Tube
- 34:25Check this list
- 35:43Summary
- 39:16Insurance Fraud
- 40:29Funny Remarks
related talks
 27mLock It and Still Lose It —on the (In)Security of Automotive Remote Keyless
 15mSoK: Stealing Cars Since Remote Keyless Entry Introduction and How to Defend...
 44mResearch Only? Understanding the Scope of Automotive...
 44mBreaking the Security of Physical Devices
 58mA Survey of Remote Automotive Attack Surfaces
 37mAutomatic Automotive Hacking
 51mRadio Hacking: Cars, Hardware, and more!
 41mGrand Theft House: RF Lock Pick Tool to Unlock Smart Door Lock