Radio Hacking: Cars, Hardware, and more!
summary
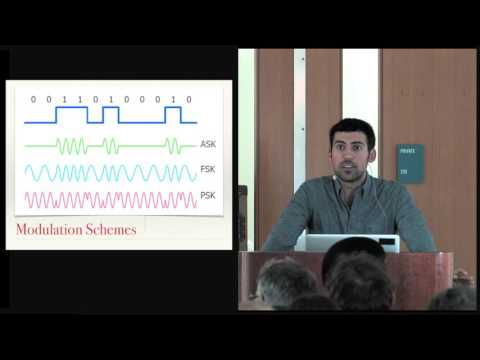
Shows actual exploits and working gear: records fixed RF garage codes and reduces brute force from ~30 minutes to 8 seconds to brute force by using de Bruijn sequences and removing inter‑packet delays, uses RTL‑SDR and HackRF plus inexpensive transmitters (yardstickone, repurposed Mattel IME) and a $30 under‑car device to capture future rolling codes. Demonstrates a rollJam attack and a Raspberry Pi MITM that finds plain or invalid SSL in car apps (about 5/10 apps accept bad certs), and the attacks reliably work in field tests.
AI-written summary · about
chapters (16)
- 0:00Introduction to RF hacking
- 2:00FCC database for security
- 5:28Radio analysis tools
- 7:32SDR software demonstration
- 10:55Analyzing garage signals
- 12:47Digital signal modulation
- 15:59Brute forcing garage codes
- 19:26Optimizing the attack
- 22:35Open sesame attack
- 25:47Garage security takeaways
- 27:23Hacking connected cars
- 31:02Mobile man-in-the-middle
- 34:58Hardware reverse engineering
- 37:37Rolling code mechanisms
- 39:33Roll jam attack
- 43:21Final takeaways and Q&A
related talks
 30mDemystifying IoT/OT Hacks With SDR
 44mBreaking the Security of Physical Devices
 59mWireless security testing with attack
 35mWireless Hacking With HackCUBE-Special
 01h 01mRapid Radio Reversing
 45m Hacking satellites with Software Defined Radio (SDR)
 30mBuilding hacking tools in JavaScript
 53mHacking the Wireless World with Software Defined Radio - 2.0