A Comprehensive Measurement Study of Domain Generating Malware
summary
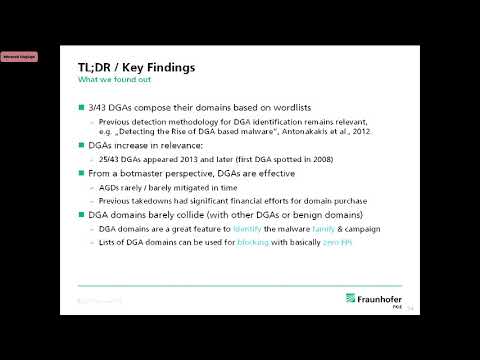
Reimplemented 43 DGAs and extracted 253 seeds to precompute about 160 million domains, then queried historical WHOIS/DomainTools records for up to 18 million of those names. Findings: only ~115,000 (≈0.6% registered) show up, GameOver P2P registers ~74k/260k (~30%), and global collisions are vanishingly rare (≈3,000 hits across the entire set), so pre-computed blocklists reliably tag families with minimal false positives; a shared dataset and web service ingest feeds for automated labeling and blocking and is already in operational use.
AI-written summary · about
chapters (19)
- 0:00Introduction
- 0:27Who thinks this domain is automatically generated
- 1:02Outline
- 1:31Domain Generation Algorithms
- 2:31Why Use Domain Generation Algorithms
- 3:45Key Findings
- 7:40Data Set
- 8:24Reverse Engineering
- 10:47Data Source
- 11:22Taxonomy
- 13:42How are domains used
- 16:40Data visualization
- 17:00Number of generated domains
- 18:05Registration numbers
- 19:33Domain takedowns
- 20:53Collisions
- 22:03Preregistrations
- 24:47Registration Log Ahead
- 27:17Conclusion
related talks
 46mExploring the ecosystem of malicious domain registrations in the .eu TLD
 59mCatching Malware En Masse: DNS and IP Style
 30mDeception at Scale: How Malware Abuses Trust
 28mFerris Bueller's Guide to Abuse Domain Permutations
 51mThe New Scourge of Ransomware: A Study of CryptoLocker and Its Friends
 43mDetecting and Preventing Malicious Domain Registrations in the .eu TLD
 25mDark Side of the DNS Force
 40mCritical DNS & Domain Name Security Intelligence to Thwart Cyberattacks