Spying on my Network for a Day: Data Analysis for Networks
summary
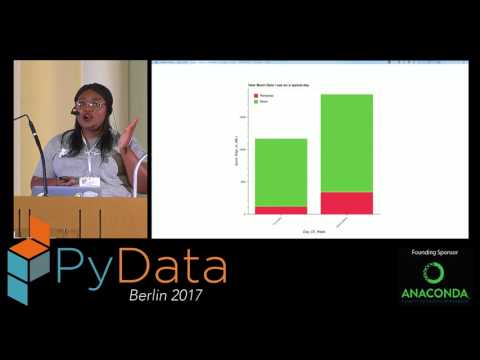
Collected one day of home packet captures (about 354 total) producing over 450,000 packets and processed with Wireshark then exported to CSV for visualization in Bokeh inside Jupyter. Analysis pinpoints major bandwidth consumers (YouTube session ~437 MB), shows DHCP broadcasts that reveal a roommate arriving, surfaces background services chewing bandwidth, and suggests automating capture with a Raspberry Pi or using Moloch for large-scale packet indexing and anomaly detection.
AI-written summary · about
chapters (10)
- 0:00Network data analysis intro
- 3:39Network experiment setup
- 4:51IP packets 101
- 9:11Daily data usage
- 12:27Packet spikes visualization
- 16:02Protocol usage patterns
- 18:50Analyze home router traffic
- 21:41Automate traffic analysis
- 24:49Personal insights from monitoring
- 25:56Q&A on home arrivals
related talks
 40mVisualizing Security
 40mUncovering Covert Channels in Your IoT Networks
 27mCollect All the Data; Protect All the Things
 14mEndangered Privacy: Large-Scale Monitoring of Video Streaming Services
 29mHow to Spy with Python
 44mInspecting IPTV for Fun and No Profit
 45mConnecting the dots to go from tabular security incident data to behavioral graph understanding
 40mThe NOC Report