Our Journey of Implementing TLS at Scale for Services on Kubernetes

summary
Describes implementing TLS for 40+ microservices on Kubernetes using Diploma (Vault-based CA) to issue certs and Chancellor (Kubernetes controller) to disburse and mount secrets, serving ~2000+ certs/day in nonprod and automating renewal and events to Wavefront. Explains migrating from Diploma v1 to v2 with an expand-contract rollout to avoid trust breaks, standardizing secret and CA interfaces, removing embedded deploy scripts, and reports a working, non‑open source production system.
AI-written summary · about
chapters (14)
- 0:00Introduction
- 0:25What we do
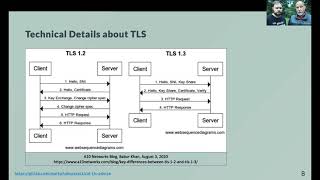
- 1:54What is TLS
- 3:26TLS identification
- 5:23Challenges
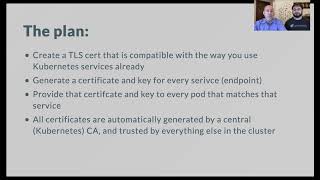
- 6:26TLS Problem Statement
- 7:02Certificate Authority
- 9:51Summary
- 10:55Scope of Change
- 13:30Chancellor
- 16:49Issues
- 17:26Expansion Pattern
- 20:35CA Features
- 23:16Questions Answers
related talks
 31mPractical TLS Advice for Large Infrastructure
 31mHow We Solved TLS at Scale: Self-Service, Multi-Tenant Cert-manager
 36mZero Trust at Shopify Scale: Automating MTLS Across Thousands of Services
 15mCertificates in Kubernetes
 01h 03mSecuring Legacy Applications and Container Microservices in Kubernetes
 15mSecuring your app's communications with Kubernetes, Azure Key Vault, and TLS certificates
 32mAchieving Mutual TLS: Secure Pod-to-Pod Communication Without the Hassle
 31mPKI the Wrong Way: Simple TLS Mistakes and Surprising Consequences