Achieving Mutual TLS: Secure Pod-to-Pod Communication Without the Hassle
summary
Claims a Kubernetes admission controller that auto-creates per-pod X.509 keys and CSR objects, approves them, and mounts signed certificates as Secrets so apps find PEM and PKCS#12 files at a known path. Uses cfssl/OpenSSL tooling background, Kubernetes mutating admission webhook API, CSR approval via the Kubernetes CA, and small Go/Java shims for gRPC and HTTP TLS. Demo shows client and server complete a mutual‑TLS RPC successfully.
AI-written summary · about
chapters (19)
- 0:00Achieving Mutual TLS
- 1:44Certificate Lifecycle
- 5:50How are Certificates used
- 6:28Golang Applications without TLS
- 7:01Golang Applications using TLS
- 7:34Java Applications without TLS
- 8:07Java Applications using TLS
- 8:54Mutual TLS in your services
- 9:26TLS keys with Kube TLS
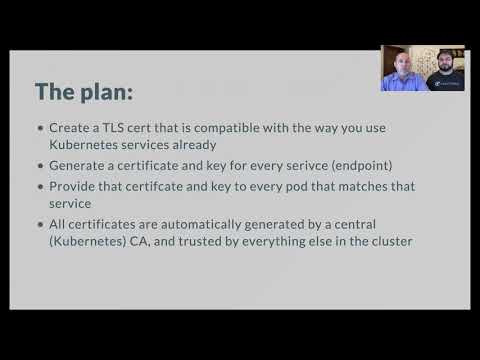
- 10:21The plan
- 11:45The details
- 17:42Mutating Webook Request Body
- 18:28Mutating Webook Response Body
- 19:31Webhook Controller
- 20:36Create And Upload Car
- 21:56Create Secret
- 25:21Using KubeTLS
- 27:06Compare to Service Mesh
- 30:38Future Directions
related talks
 38mImproving Secure Pod-to-Pod Communication Within Kubernetes Using...
 15mSecuring your app's communications with Kubernetes, Azure Key Vault, and TLS certificates
 46mContinuous Kubernetes Security
 31mPractical TLS Advice for Large Infrastructure
 27mPragmatic Pod Patterns: Leveraging sidecar containers in Kubernetes
 31mPKI the Wrong Way: Simple TLS Mistakes and Surprising Consequences
 24mOur Journey of Implementing TLS at Scale for Services on Kubernetes
 24mOne stop talk for kubernetes security !!