Mobilized Immobilizer - Bypassing Motorcycle Security 1
summary
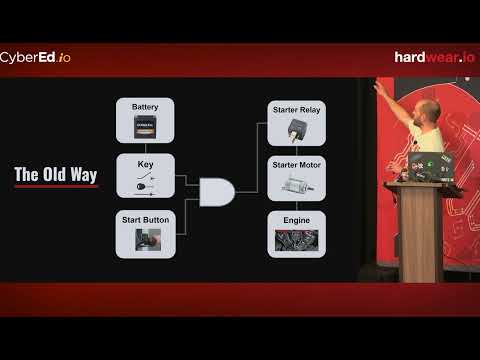
Reverse engineers a 2025 Indian Scout Bobber to extract CAN traffic with a Kvaser and CAN Pico, finds two nested challenge‑response exchanges that reduce to simple XOR operations, recovers the engine and PIN secrets, and identifies two physical kill wires that force shutdown. Builds a seat‑under hardware implant that injects seeds, forces the WCM into an error loop, disables shutdown and ultimately starts the bike without a key; seven CVEs issued.
AI-written summary · about
chapters (7)
- 0:00Introduction and speaker background
- 10:05Motorcycle security basics
- 16:06CAN bus protocol explained
- 20:22Finding seed and key authentication
- 27:09Bypassing immobilizer security
- 33:52Hardware implant demonstration
- 40:46Research outcomes and CVEs
related talks
 44mMy Car, My Keys: Obtaining CAN Bus SecOC Signing Keys
 37mAutomatic Automotive Hacking
 50mAdvanced CAN Injection Techniques for Vehicle Networks
 43mSecuring the Connected Car
 40mD2T1 - Backdooring & Remotely Controlling Cars
 39mBackdooring Hardware Devices by Injecting Malicious Payloads on Microcontrollers
 27mLock It and Still Lose It —on the (In)Security of Automotive Remote Keyless
 41mSecrets Of Simos18: REng The Secure Boot Mechanism Of An ECU