Detect and track the aliens hiding in your dependencies

summary
Shows how to detect and track vulnerable open‑source dependencies by using OWASP DependencyCheck in a Jenkins pipeline to generate reports and push results into OWASP DependencyTrack for portfolio management. Demonstrates a Jackson XML external‑entity vulnerability and fixes it by upgrading library versions; notes DependencyCheck supports Java/.NET (and experimental Ruby/Node/Python) and DependencyTrack runs as a Docker service (defaults to H2, ~4GB RAM).
AI-written summary · about
chapters (8)
- 0:00Introduction
- 1:53OWASP foundation
- 3:16Vulnerability databases
- 5:46Detection tools
- 10:02XXE demo
- 14:22Jenkins integration
- 17:51Results and false positives
- 19:10Conclusion
related talks
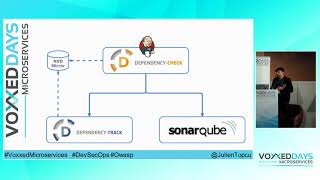 27mFind and Track the hidden vulnerabilities inside your dependencies
 14mDetect and Track the Zergs in Your Dependencies!
 17mDetect and Track the Vulnerabilities Hiding in Your Dependencies
 29mFlagship Projects: Dependency-Check
 54mSupply Chain Sec /w Dependency Track
 24mDependency Track Fortifying The Supply Chain
 46mSafely through the dependency minefield using OWASP Dependency Track
 20mDependency Analytics