Detect and Track the Vulnerabilities Hiding in Your Dependencies

summary
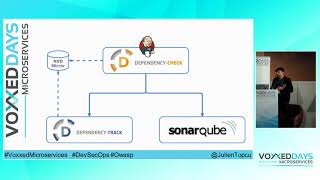
Explains how open-source library vulnerabilities are cataloged (NVD, CVE) and scored (CVSS), then demonstrates building a Continuous Security pipeline in Jenkins using OWASP Dependency-Check to detect vulnerabilities and OWASP Dependency-Track to track them, enabling a first step toward DevSecOps.
AI-written summary · about
chapters (8)
- 0:00Introduction
- 1:25OWASP tools overview
- 2:27Dependency-Track demo
- 8:02Fixing detected vulnerabilities
- 10:12JavaScript and npm support
- 10:57Jenkins integration
- 13:22Advanced features and notifications
- 14:27Q&A
related talks
 27mFind and Track the hidden vulnerabilities inside your dependencies
 20mDetect and track the aliens hiding in your dependencies
 11mIdentifying Security Vulnerabilities at Scale: Venture Inside a Pipeline
 14mDetect and Track the Zergs in Your Dependencies!
 34mDependency Track
 29mFlagship Projects: Dependency-Check
 46mSafely through the dependency minefield using OWASP Dependency Track
 01h 18mDevSecOps - Automating Security in DevOps