Dependency Track Fortifying The Supply Chain
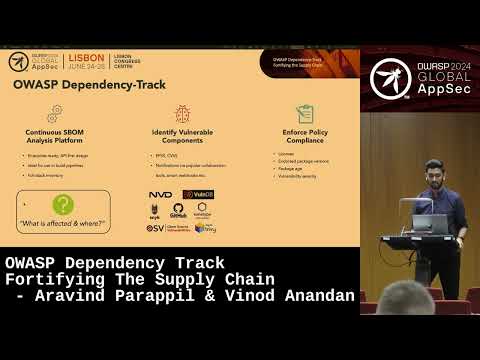
summary
Enterprise evidence: Dependency Track ingests CycloneDX SBOMs and continuously scans components so the build inventory is live not static. The talk gives hard numbers — 91% of codebases are 10+ versions behind, vulnerabilities persist 2.8 years on average, 29% of Log4j downloads remain vulnerable (~75M) — and demos show EPSS prioritization, a policy engine that auto-fails or auto-suppresses findings, integrity analysis comparing hashes to Maven/PyPI, and a Hades rearchitecture for 80k–100k projects.
AI-written summary · about
chapters (9)
- 0:00Supply chain risks
- 3:21Software bill of materials
- 6:58Dependency Track overview
- 9:48Dashboard walkthrough
- 13:21Vulnerability suppression
- 15:50Policy and license tracking
- 17:36Enterprise config and integrations
- 19:23Project Hades scale
- 22:59Community contributions
related talks
 54mSupply Chain Sec /w Dependency Track
 46mSafely through the dependency minefield using OWASP Dependency Track
 14mSupply Chain Security, why should I care?
 26mKnow Your Dependencies: A Guide to Automating Dependency Assurance
 25mFlagship Projects: Dependency Track
 23mSupply Chain Security using Free and Open Tools
 36mBuilding a Trusted and Resilient Software Supply Chain
 32mAdapting DevOps in a World of Growing Software Supply Chain Attacks