Using SELinux with container runtimes

summary
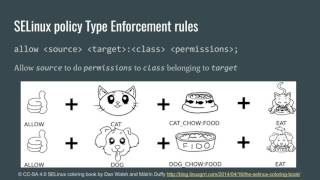
Explains how SELinux uses type enforcement plus MCS categories to isolate containers and block escapes, and demonstrates that relabeling mounts or disabling SELinux is unsafe. Shows podman commands: podman inspect -l, podman run with a custom security label, and watching audit denials when a container tries to read /etc/shadow or access docker sockets. Presents a tool udica that inspects container JSON, generates SELinux policy blocks, and loads a module so a container labeled container_t variant can read /home, access /var/spool, and bind port 21.
AI-written summary · about
chapters (24)
- 0:00Introduction
- 0:38Type enforcement
- 3:36Containers
- 4:28Container runtimes
- 8:29Breaking into the system
- 12:21MCAS
- 16:05Reliable
- 17:17Problems
- 18:25Current solution
- 19:08Second solution
- 20:20Request for custom policies
- 21:08Fishinger
- 21:32Example container
- 26:06Demo
- 27:12Base
- 28:11Pool
- 29:01Repository
- 29:19Installation
- 29:39Message of the Day
- 31:10Whats Next
- 33:07Loose vs Type
- 35:44Private Directory
- 36:46Inspection
- 40:11Firefox