0-days & Mitigations: Roadways to Exploit and Secure Connected BMW Cars
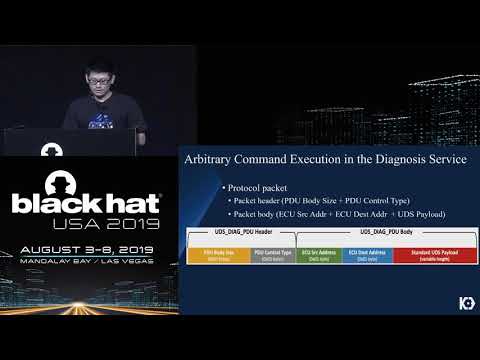
summary
Researchers disclose multiple exploitable bugs: a race condition in the diagnostic service lets an attacker win a TOCTOU to write a signed update and get root via USB or OBD; a stack buffer overflow in navigation map update (no canary, ASLR off) yields code execution; a provisioning MD5/HTTP flaw plus hardcoded NGTP keys and SMS triggers let a fake GSM (USRP/OpenBTS) force updates, exploit an out‑of‑date WebKit UAF for a browser shell, escalate to CAN transmit and craft UDS to reach other ECUs; mitigations roll out OTA—86% first attempt, 96% after retries.
AI-written summary · about
chapters (10)
- 0:00Introduction and agenda
- 1:00Background and timeline
- 2:58BMW vehicle components
- 7:26Rooting the head unit
- 14:00Navigation update attack
- 16:27Telematic box exploitation
- 23:05Telematic box vulnerability
- 29:39Gateway and ECU attack
- 37:12BMW incident response
- 44:22Countermeasures and takeaway
related talks
 40mPerfektBlue: Universal 1-click Exploit to Pwn Automotive Industry…
 37mAutomatic Automotive Hacking
 40mUnlocking the Drive: Exploiting Tesla Model 3
 41mPanel: Tackling Automotive Hardware Vulnerabilities
 40mSecuring the Connected Car
 43mSecuring the Connected Car
 44mExposing Critical Threats In Millions Of Connected Devices
 41mKeynote Presentation: Ten Years After the Jeep Hack: A Retrospective on...