How to Leak a 100-Million-Node Social Graph in Just One Week?
summary
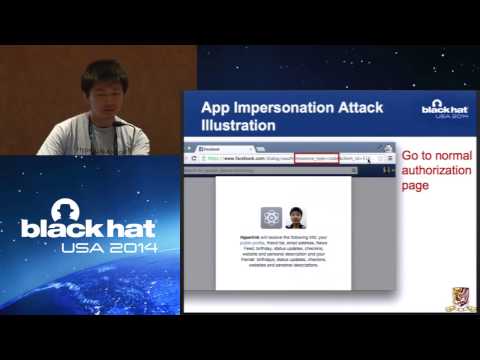
Demonstrates an OAuth 2.0 implicit-authorization-grant flow + bearer-token abuse that lets an attacker obtain app access tokens without the app secret, then use them to impersonate privileged apps. Uses simple browser scripts and cURL on AWS instances to crawl API endpoints; on one Facebook‑like OSN the attack collects a 100‑million‑user social graph in under a week for about $150, exploiting a privileged app with >1M queries/hour and coarse scope/rate controls.
AI-written summary · about
chapters (21)
- 0:00Introduction
- 0:40Whats the problem
- 1:42Basic protocol
- 2:53Key idea
- 3:57Consequences
- 5:09Earth
- 9:32Conclusion
- 10:31Implicit Flow
- 11:48Token Type
- 15:38Feedback
- 16:17The Problem
- 17:41Factors
- 18:40App Impersonation Out
- 19:24How to Fix
- 21:41Protection
- 23:19Refresh Token
- 25:17App Impersonation Prevention
- 26:03Programmers are lazy
- 27:04Developers use the right way
- 28:34Facebook
- 29:25App Secret