Abusing Microsoft Kerberos: Sorry You Guys Don't Get It
summary
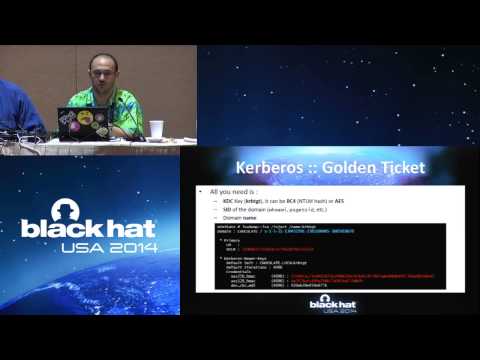
Demonstrates concrete attacks using Mimikatz to read Kerberos keys from LSASS memory, inject NTLM/AES keys, and forge tickets; recovers a krbtgt key that often hasn’t changed since 2005 and uses it to create golden tickets (default 10‑year lifespan) that let a non‑domain machine obtain TGTs/TGS and access shares — including disabled or nonexistent accounts — exploiting a ~20‑minute KDC revalidation window; shows overpass‑the‑hash to create valid TGTs from NTLM/AES hashes.
AI-written summary · about
chapters (5)
- 0:00Intro
- 1:17A little reminder
- 16:28Kerberos :: TGT & TGS
- 25:29Kerberos :: Golden Ticket
- 37:43Thank you all!
related talks
 45mYou « try » to detect mimikatz
 58mHacking in 2016 - How is our systems broken?
 50mWatching The Watchdog: Protecting Kerberos Authentication With Network Monitoring
 40mExploiting Windows Hello for Business
 40mThe Attacker’s Guide to SSO and Passwordless Technologies
 35mWalking Your Dog in Multiple Forests - Breaking AD Trust Boundaries through Kerberos Vulnerabilities
 47mFinding a Needle in an Encrypted Haystack
 41mBreaking Kerberos' RC4 Cipher and Spoofing Windows PACs