Crypto-Agile PKI: A Strategic Blueprint for Post-Quantum Trust
summary
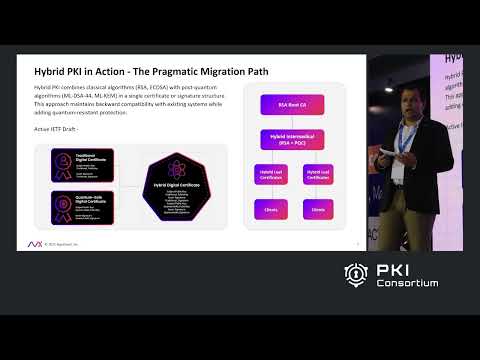
Blueprint offers concrete steps: inventory TLS, S/MIME, code signing and device identities; test hybrid certificates that embed ML-DDSA-44 plus RSA and show two signatures in one cert so browsers can fall back; measured chains at ~8 KB for hybrid versus ~14 KB for full PQC, giving ~45% smaller size while still ~5x larger than classical RSA; lab demos succeed with zero-touch ACME-based issuance and short-lived certs; align governance to draft-ietf-lamps-x509-slhdsa-09, NIST 1800-38B, ETSI and CAB Forum; surveys show ~62% exploring hybrid and ~40% browser/site support.
AI-written summary · about
chapters (8)
- 0:00Welcome
- 2:48Quantum threat to encryption
- 7:23PKI migration challenges
- 10:40Hybrid PKI necessity
- 16:27Hybrid PKI adoption examples
- 19:19Crypto-agility benefits
- 21:04Crypto-agile PKI pillars
- 22:29Q&A
related talks
 20mHybrid Approach for quantim safe PKI Development for Organizations HAPKIDO
 13mNavigating the Quantum Readiness Journey: Open-Source Cryptography, PKI and Signing Tools
 32mand Signatures – no Problem?
 36mPost-Quantum Cryptography for Digital Signing
 15mOne App at a Time: DigiCert's Practical Playbook for the Post-Quantum Transition
 23mELI5: Implementing Digital Certificates for a Post-Quantum World
 38mPKI deployments are as unique as any snowflake; how to build equally flexible PQ migration strategie
 19mAgile is the new black – Why Preparing for Postquantum Crypto also Matters to You!