Embracing Zero Trust When You Aren't the World's Largest Internet Company

summary
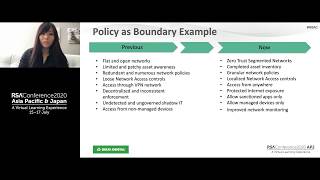
Zero trust is practical not mythical: organizations repurpose existing directories, asset and configuration databases, and endpoint protection to make per-request access decisions. Immediate wins come from protecting user-facing endpoints by inventory endpoints and services, strengthening auth with MFA and device attestation as well as strengthen authentication practices, and placing programmable enforcement points driven by a policy engine that consumes signals from NAC, EDR and CMDBs — in short use NAC and endpoint protection to block credential abuse and lateral movement.
AI-written summary · about
chapters (15)
- 0:00Introduction
- 2:45Thinking in Systems
- 3:45Zero Trust
- 4:57Machine to Machine Security
- 5:45History of Zero Trust
- 6:48Boundaries
- 9:46Google
- 10:47Trust but Verify
- 11:40Trust Wall
- 12:40Why Authentication Matters
- 19:43Threat Models
- 24:08Use Cases
- 24:35Question
- 28:03Boring things
- 28:20Jeremiah Grossman
related talks
 45mZero Trust: Getting to Step One..and What to Do When You Get There
 02h 48mZero Trust: the new normal!
 40mZero Trust, Zero Pain: A Practical Implementation with Intrinsic Security
 40mZero Trust and Privacy: Moving Security Closer to the Target
 18mRedefining Cybersecurity: Harnessing Zero Trust Architecture for a Resilient Future
 40mLessons From Our Zero Trust Journey: Successes, Failures & Dodging Pitfalls
 27mA Simplified and Practical Approach to Pursuing a Zero Trust Architecture
 40mZero Trust in a Post-pandemic World