Enforcing a Secure Supply Chain on Kubernetes
summary
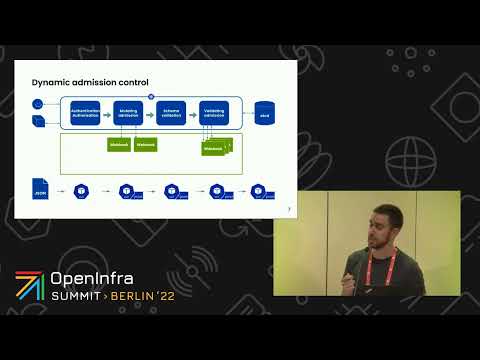
Explains a concrete pipeline: use cosign + Fulcio + Rekor to produce signatures (including keyless OIDC signing from GitHub Actions), push signatures to OCI registries and Rekor, then enforce verification in-cluster via an admission controller implemented as a WebAssembly policy module. The controller mutates incoming Pod specs to replace mutable tags with verified digests and rejects pods whose images or wasm policies lack valid signatures or provenance; CI-integrations and materials lists let teams detect vulnerable or untampered dependencies before they run.
AI-written summary · about
chapters (14)
- 0:00Introduction
- 0:13What is a supply chain
- 1:19systo
- 2:56keyless
- 3:57keyless signing example
- 4:51github action
- 5:41dynamic admission controller
- 7:32policy engine
- 9:40sign and verify
- 11:02secure all containers
- 12:25instantiate in cluster
- 12:45instantiate in pod
- 13:09whats next
- 14:08outro
related talks
 35mEnforcing a Secure Supply Chain on Kubernetes
 40mEnforcing a Secure Supply Chain on Kubernetes
 23mSoftware Supply Chain Integrity with Sigstore
 36mKubernetes Supply Chain Security: The Software Factory
 34mMake the Secure Kubernetes Supply Chain Work for You
 01h 27mSupply Chain Security Tooling
 20mSimplifying Kubernetes: Streamlining Secure App Deployment in DevSecOps
 42mDid you sign this (image)?