A mechanism to isolate CPU topology information in the Linux kernel -- CPU Namespace
summary
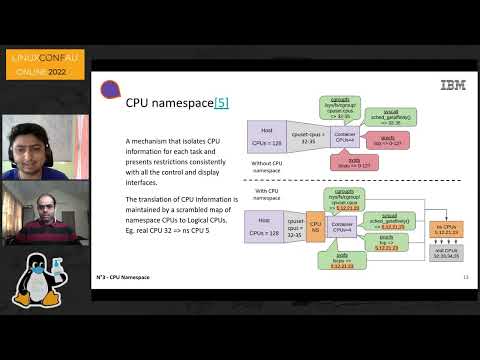
Proposal implements a kernel-level CPU namespace that maps namespace CPU IDs to real logical CPUs (proof-of-concept patches, new clone flag to create namespaces), makes /sys /proc /cgroupfs and sched_set/getaffinity context-aware, and can use a scrambled CPU map to obfuscate topology. Tested on an IBM Power9 (44 SMT4 containers on 176 CPUs) with nginx + wrk: memory at init -91%, peak -89%, throttle -74%, latency -13%, throughput +20.73%, showing tangible benefits and open questions around NUMA, time-based quotas, and namespace–cgroup interactions.
AI-written summary · about
chapters (10)
- 0:00Introduction
- 1:15Agenda
- 1:40Background
- 4:20Fair use
- 5:05Solutions
- 9:32CPU Namespace
- 11:56Performance
- 15:56Proof of concept
- 20:03Challenges
- 23:11Questions
related talks
 01h 03mLinux Namespaces for Fun and Isolation
 15m(Impact of) Recent CPU topology changes
 47mLinux user namespaces: a blessing and a curse
 57mNamespaces for Security
 23mCPU Isolation state of the art
 54mUnderstanding user namespaces
 25mCPU isolation tuning through cpuset
 32mIsolation aware smp_call_function/queue_work_on APIs