What You Need to Know About Open Source - Trust Me, I'm a Lawyer

summary
Covers practical license choices and concrete risks: walks through MIT/BSD permissive versus Apache 2.0 patent grant and its automatic termination “poison pill,” GPL family differences including Affero GPL triggers on SaaS and LGPL dynamic vs static linking, plus why missing LICENSE files mean “read‑only” code. Explains business models (sell support, trademark, warranties), contributor CLAs vs ownership assignment, and recommends scanners like WhiteSource/Black Duck; slides are on SpeakerDeck. Watch if license compatibility, patent exposure, or contribution policies matter.
AI-written summary · about
chapters (12)
- 0:00Introduction to legal issues
- 1:45Defining open source
- 7:08Rights and obligations
- 11:49Intellectual property basics
- 15:35Commercializing open source
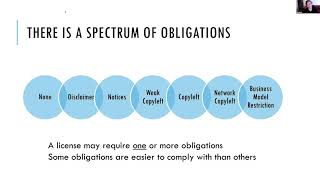
- 18:55The OSI and license spectrum
- 21:16MIT and BSD licenses
- 24:19BSD nuances and limitations
- 29:31The Apache 2.0 license
- 31:35GPL and copyleft licenses
- 37:30License compatibility
- 38:46Managing OSS in the enterprise
related talks
 01h 04mWhat You Need to Know About Open Source—Trust Me, I’m a Lawyer
 57mWhat You Need to Know About Open Source—Trust Me, I'm a Lawyer
 01h 11mWhat You Need to Know About Open Source—Trust Me, I'm a Lawyer
 51mThe Impact of Leveraging Open Source
 42mOpen Source Licenses: Between Parish Wars and Radicalism
 01h 38mOpen Source Licensing: Types, Strategies and Compliance
 37mIntro to Open Source Licensing
 28mLicence to Code: Understanding open source licenses for developers