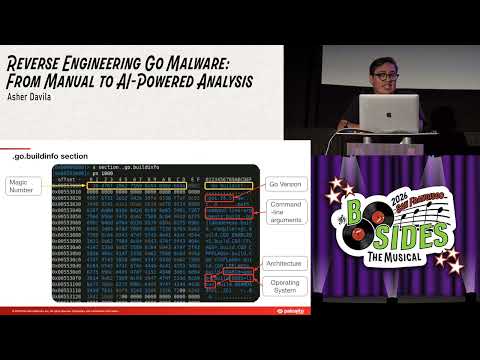
Reverse Engineering Go Malware: From Manual to AI-Powered Analysis
summary
Shows step-by-step reverse engineering of Go IoT malware (BotenaGo, PumaBot) using Ghidra, Radare2, r2ai and GhidraMCP to rebuild strings and payloads and map C2 behavior; demonstrates why Go binaries explode in size and function count, how to locate the go PC line table parsing and go build info, and shares an open‑source r2 script that recovers symbols. Covers MCP/agent workflows (Sidekick, R2MCP), successful SSH brute‑force mapping, and recurring failures like misidentified crypto and unpacking limits.
AI-written summary · about
chapters (13)
- 0:00Introduction to talk
- 0:50Why Go is popular for malware
- 5:30Key differences between Go and C binaries
- 8:19Go build info and PC line table
- 12:15String handling in Go malware
- 14:24AI-assisted tooling with R2AI and DK
- 19:02MCP servers and agents for analysis
- 22:14Case study: Pumatronics IoT malware
- 27:17AI analysis of GreenBlood ransomware
- 33:44AI orchestrators and dynamic analysis
- 35:51ReverseMe CTF challenge hint
- 36:54Key takeaways and recommendations
- 40:28Closing and Q&A session
related talks
 27mA Deep Dive into Go Malware: Using Metadata to Empower the Analyst
 32mThe Dark Side of Go: A 2020 Go Malware Round Up
 54mMaking oRAT Go...Further
 33mBasic Malware Analysis for Incident Responders
 45m"Advanced Malware Threat: handling obfuscated code using..."
 40mAnalyzing Windows Malware on Linux: Getting Started Tips and Examples
 01h 03mThe Dark Side of Malware Analysis
 29mA Day in the Life of a Mobile Malware Reverse Engineer