Hunting Malicious IDE Extensions: Building Detection at Scale... (Vinod Tiwari)
summary
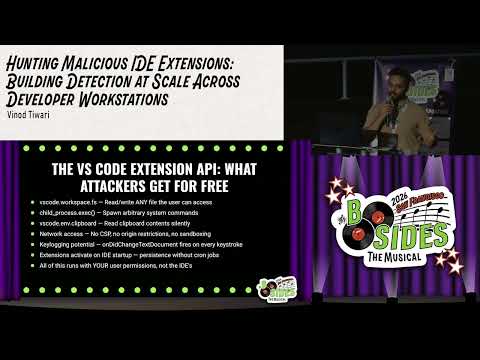
Developer workstations run IDE extensions with full user privileges across VS Code Cursor and JetBrains so a detection pipeline is built that inventories extensions via Jamf + bash script, matches them to an allowlist and sends Slack alerts; scanning 32 devs on ~30 hosts finds 556 unique extensions and >1,000 total with one user running 157. Extensions expose APIs like Workspace FS and child_process/clipboard so a scanner called ID viewer scores permissions, emits JSON, and flags risky installs.
AI-written summary · about
chapters (10)
- 0:00Introduction
- 0:24Why malicious IDE extensions
- 3:09Developer workstations blind spot
- 7:02Extension permissions explained
- 12:43Red flags in extension metadata
- 15:10Building detection at scale
- 18:38MDM and EDR limitations
- 19:19Introducing IDE viewer
- 21:43Takeaways and recommendations
- 22:46Q&A session
related talks
 46mVSCorode: Inside Your IDE, Inside Your Git Repository
 36mExploiting Vulnerabilities and Flaws to Attack Supply Chain
- 46mVSCorode: Inside Your IDE, Inside Your Git Repository
 20mDependency Analytics
 58mWriting VS Code extensions for fun and profit
 21mSecurity begins with secure development environments
 40mMarkDoom: How I Hacked Every Major IDE in 2 Weeks
 31mShadow IT Battlefield: The CyberHaven Breach and...