A Manufacturer's Post-Shipment Approach to Fend-Off IoT Malware in Home Appliances

summary
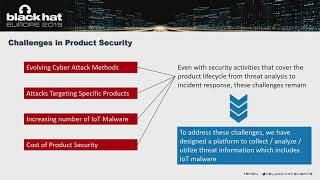
Manufacturer runs a physical honeypot network for over 5 years and turns captured IoT malware into analyzed signals via a sandbox plus MITRE ATT&CK mapping and statistical visualization to inform development and testing. The AA platform feeds vulnerability prioritization and reduces test scope; clustering yields a reduced corpus (for ARM ~1,800 ARM samples clustered) for device execution. A built on-device blocker called STR self-protection is lightweight, shows up to 86% detection in evaluations on real devices with minimal runtime impact.
AI-written summary · about
chapters (7)
- 0:00Post-shipment IoT security
- 2:37IoT malware threats
- 5:33IoT threat intelligence platform
- 12:24STRIN self-protection concept
- 17:52Business unit collaboration
- 20:06Manufacturer security outlook
- 23:03Conclusion & Q&A
related talks
 29mUnderstanding the IoT Threat Landscape
 22mExpert Insights | Keynote
 21mIndustrial IoT security issues and countermeasures
 20mKeynote: Outsmarting IoT Defense: The Hacker's Perspective
 32mCommon Attacks on IoT Devices
 30mThe Hunt for Major League IoT-ICS Threats: A Deep Dive into IoT Threat Terrain
 41mUnique Challenges Of Security Programs For Hardware/IoT Makers
 20mCatch Attackers Before They Strike with AI-powered Threat Intelligence