The Hunt for Major League IoT-ICS Threats: A Deep Dive into IoT Threat Terrain

summary
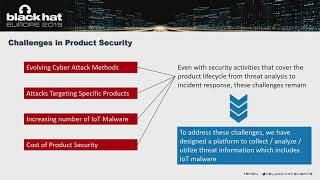
Claims a deployed pipeline that ingests 25 TB of traffic, runs 350+ global hunting engines and an hourly automatic workflow that detected over 1.1 billion attacks, collected 400M+ suspicious IPs, 30M+ domains and 1M+ malware samples of which ~40% are unknown. Describes concrete tooling: protocol handlers for 30+ IoT/ICS protocols, S3/ECS storage, session-closure PCAP analysis, blacklist generation and one-click deployment of new hunting images. Shows case counts, botnet device estimates (≈1.1M), examples of high‑interaction honeypots and results of automated blocking.
AI-written summary · about
chapters (15)
- 0:00Start
- 2:23Why Perform Automated Threat Hunting?
- 3:18The Benefits of Automated Threat Hunting
- 7:302. The Hunting Agent
- 8:37Malware Crawler and Session Crawler
- 10:34Malware Analyzer
- 11:19Threat Intelligence based on Athena
- 12:00One-Click Deployment/Re-Deployment
- 18:01Highlights of the loT-ICS Hunting System
- 19:36loC Hunting as A Service
- 21:15Global Botnet Analysis and Alert
- 22:29Unknown Malware Playground
- 24:001-Day/Unknown Vulnerability Hunting
- 25:38The Threat of Next Generation
- 28:41Closing Remarks
related talks
 29mUnderstanding the IoT Threat Landscape
 47mTrend Micro's VP of security research reveals the latest IoT threats and how to combat them
 40mInto the Mind of an IoT Hacker | How to Protect IoT Networks & Devices
 43mIoT Security Challenges and Solutions
 23mYour xIoT Devices Are Under Attack: Why everything connected is now a target
 52mThe Industrial Cyberthreat Landscape: Year in Review Report with Updates
 27mThe IoT storm... Will we survive the coming deluge?
 42mCloudy With a Chance of Exploits: Compromising Critical Infrastructure Through IIoT Cloud Solutions