The Promise of Trustworthy AI

summary
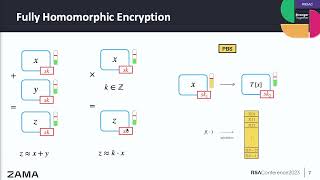
Claims that models improve without ever collecting raw data by combining Federated Learning with Homomorphic Encryption, demonstrating encrypted weight aggregation (simple additive demo) and citing the 2019 NeurIPS “Deep Leakage from Gradients” attack as the leak FHE closes. Uses lattice‑based, quantum‑resistant crypto and tools like Microsoft SEAL, OpenFHE and HEIR; research shows up to ~1,000× speedups for some HE ops, and on‑device examples (Gboard) validate the approach for practical private collaboration.
AI-written summary · about
chapters (13)
- 0:00Welcome
- 2:47Trustworthy AI matters
- 7:23Privacy in AI interactions
- 9:13AI model building
- 12:19Federated learning
- 16:38Privacy gap in federated learning
- 18:24Data states and encryption limits
- 20:56Homomorphic encryption demo
- 25:41How homomorphic encryption works
- 26:24Homomorphic encryption trends
- 29:22Federated learning + homomorphic encryption
- 30:24Trustworthy AI by design
- 31:50Q&A
related talks
 52mMachine Learning over Encrypted Data with Fully Homomorphic Encryption
 40mTrust No One
 15mKeynote: Trustworthy AI with Confidential Computing
 19mPrivate AI: Building Trust Through Verifiable Computation
 44mIP Protection and Privacy in LLM: Leveraging Fully Homomorphic Encryption
 08mLLMs Without Leaks: Keep Your Code, Data & IP
 45mCrypto-AI: A Guide to Building Private and Decentralized AI Systems
 39mTrust Cards For AI