Cyber Resiliency Through Firmware Protections & Supply Chain Security
summary
Covers NIST’s PFR Guidelines and the Trusted Computing Group’s standardization efforts for using “dynamic trust” to protect firmware and improve supply-chain security for embedded systems, and explains the implications of those technologies and capabilities for embedded system security.
AI-written summary · about
chapters (11)
- 0:00Intro
- 0:39Critical Firmware Applications to Protect
- 3:36Cyber Resiliency Gap
- 5:43Resiliency Cycle
- 8:47Resiliency Standards
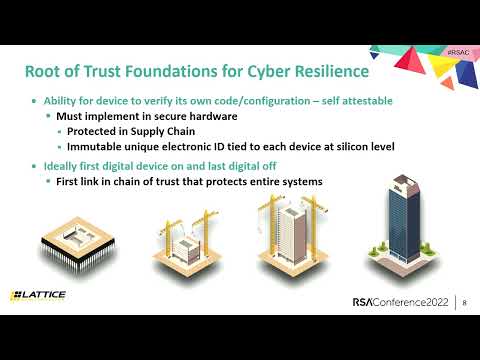
- 10:31Root of Trust Foundations for Cyber Resilience
- 12:34Example: PFR Applied to Servers
- 21:57Example Supply Chain Attacks
- 26:16How to Reduce Supply Chain Risk Profile
- 31:09Summary: Pulling it All Together
- 32:39Applying this for your Organization
related talks
 43mDevice Security in IoT
 26mKeynote: Trusted Firmware – Build Security Collaboratively
 30mSupply Chain Security for IoT Devices
 40mBuilding Resilience Standards, Resiliently
 29mEnabling a secure IoT from design to deployment
 21mIndustrial IoT security issues and countermeasures
 45mBuilding a Secure IoT Device
 40mBuilding Trust in Supply Chains