"Connecting the Dots" of NIST 800-207, TIC 3.0, and More Using SAFE

summary
Explains how the SAFE reference architecture can be used to map and apply controls from Zero Trust (NIST SP 800-207), TIC 3.0, and other security frameworks to create a practical roadmap for implementation. Covers the capabilities of those frameworks and demonstrates using SAFE to simplify and connect their requirements into an executable security plan.
AI-written summary · about
chapters (12)
- 0:00Introduction to SAFE
- 1:01Process over products
- 2:31Complexity in security
- 4:35Bridging the effectiveness gap
- 7:21Avoiding silos of excellence
- 9:23The SAFE architecture key
- 11:35Defining business flows
- 14:41Applying TICC 3.0 principles
- 23:14Zero trust architecture
- 26:32Maturity modeling
- 30:33Implementation strategy
- 34:36Q&A and closing
related talks
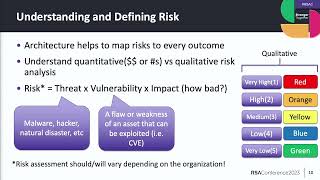 49mWhy Having a Security Reference Architecture Matters!
 35mRevolutionizing Cyber Defense: The NIST CSF 2.0 Advantage
 55mA NIST 800-207 Playbook: Zero Trust from the Whiteboard to the Boardroom
 40mThree’s Company: Unpacking and Settling in with Three NIST Frameworks
 51mHow Sworn Enemies Found a Truce (Sort of) to Achieve NIST Compliance
 50mIt’s a Journey…Where is NIST Headed with the Cybersecurity Framework
 40mCreating Cloud Native Security
 49mNIST Cybersecurity Framework v2.0: What’s changing?