Security Challenges in Direct Threat Environments
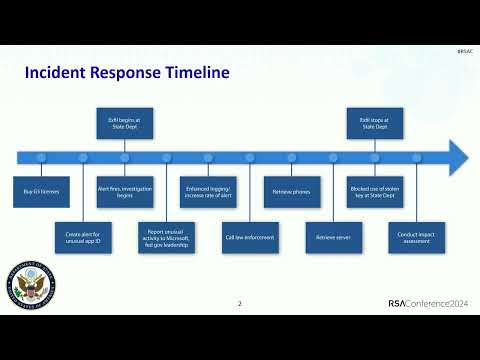
summary
Custom alert big yellow taxi on G5 telemetry detects a pattern that leads to an IP and a seized VPS; analysis finds a stolen Microsoft certificate used to mint tokens, causing unauthorized Office 365 access across 22 organizations, 500+ people. SOC speeds logging to 15-minute windows, invalidates tokens, and special agents obtain preservation through DOJ to analyze the VPS. Microsoft remediates by revoking the certificate and tokens; forensic review finds no classified data accessed.
AI-written summary · about
chapters (10)
- 0:00State Department cybersecurity mission
- 5:39Security Operations Center overview
- 10:40China-linked email breach
- 15:20Alert analysis and escalation
- 21:01Leadership notification and coordination
- 27:12Mobile device compromise theories
- 33:10Unauthorized access realization
- 37:49Threat actor infrastructure analysis
- 41:05Breach containment and remediation
- 45:42Post-incident lessons and priorities
related talks
 51mThe Enemy Within: Modern Supply Chain Attacks
 48mHacking Exposed: Next-Generation Tactics, Techniques, and Procedures
 40mFighting Where They Aren't: How Attackers Avoid Endpoints in Modern Attacks
 09mIT Security Conference 2025 | Edgar Coutinho & David Marques | Logicalis
 48mLateral Movement in the Age of Hybrid Cloud
 55mAzure Attacks Unpacked: Real-World Threats & Lessons
 52mUncovering Azure's Silent Threats: A Journey Into Cloud Vulnerabilities
 41mUncovering Azure's Silent Threats: A Journey into Cloud Vulnerabilities