Cloud Security Novice to Native in 10 Steps: A CNAPP Approach
summary
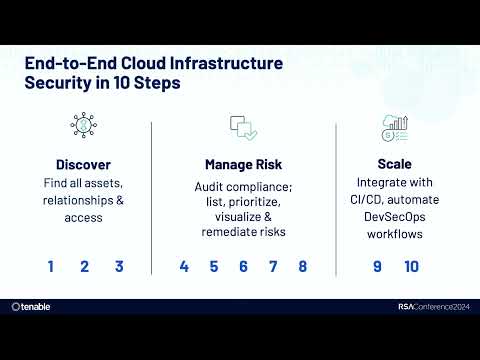
Claims a CNAPP unifies CSPM, CWPP, CIEM, KSPM and CDR into one platform and walks through 10 steps across discovery, risk management and scale. Demonstrates queries that find a toxic combination — public VM + critical CVE + overprivileged IAM role — visualizes blast radius, offers remediation code or automated fixes, and adds just in time privilege requests. Cites 95% of orgs reporting cloud breaches, shifts left into CI/CD, and licenses by average compute workloads over the last 30 days.
AI-written summary · about
chapters (10)
- 0:00Cloud security challenges
- 4:20Why cloud security is hard
- 9:39What is CNAPP
- 13:3010 steps of CNAPP
- 20:37Toxic combinations in practice
- 26:40Just-in-time access and zero trust
- 30:12Shift security left into CI/CD
- 32:22Why CNAPP works
- 35:35Next steps for your org
- 36:48Q&A on licensing and integration
related talks
 56mNavigating the Cloud Native Security Landscape
 37mCloud Native Security 101 - Introduction, Workflows and Best practices
 18mBEYOND DevSecOps – Future Journey of Security Controls
 34mCloud Native Security 101: Building Blocks, Patterns and Best Practices
 58mCloud Attack Surface Management
 18mManaging your cloud security universe as one
 40mCreating Cloud Native Security
 40mCloud Native Security: A New Paradigm for a New World