Post-Quantum Cryptography & Trust Services
summary
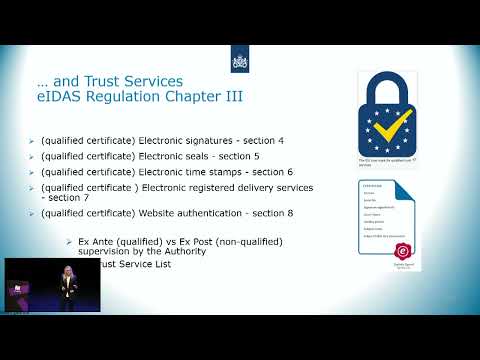
Dutch supervisory authority for trust services maps concrete actions: nine qualified providers on the EU trust list, sharing ETSI and NIST guidance, using Mosca’s-inequality timeline and a 2030+ breakage estimate for public-key threats, and refusing to mandate specific PQC choices while auditing risk assessments and migration plans. Published joint research with DIIC and TNO on quantum sensors, prototypes a quantum radar, and builds a quantum board game to train stakeholders; practical tools and timelines, not slogans.
AI-written summary · about
chapters (8)
- 0:00Welcome
- 1:55Dutch digital infrastructure authority
- 8:06IAS regulation and trust services
- 13:34Quantum program goals
- 22:40Quantum threats and migration
- 26:19Q&A
- 28:50Quantum board game
- 31:17Closing
related talks
 35mETSI ESI and Quantum-Safe Cryptography
 51mQuantum Safe Computing for Telecommunications
 19mQuantum Security and Beyond – for Digital Sovereignty and a Secure Future
 26mGet Fit For The Qubit: The Dutch approach to a Quantum Secure Society
 27mHow ETSI is Preparing for PQC
 44mQuantum Cyber Risk: How Deep and How Wide?
 27mQuantum Safety Timelines in the Financial Sector
 30mNavigating the Quantum Era – A Strategic Path to Resilience