Why FIDO Security Keys & Webauthn are Awesome

summary
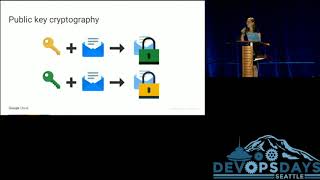
FIDO/WebAuthn replaces passwords with public‑key auth: servers store a public key, devices keep a private key and sign server challenges. Hardware comes as USB/NFC/Bluetooth dongles or built‑in secure enclaves with biometrics; protocols are CTAP1 and CTAP2 under WebAuthn. Practical notes: GitHub and Google support keys, SoloKeys and YubiKeys work, server code needs to handle array buffers and a 19‑step verification (an 850‑line example patch), and store credential ID and signature count to detect clones. iOS support is still catching up.
AI-written summary · about
chapters (17)
- 0:00Intro
- 0:35About Jen
- 2:41Authentication
- 11:09Public Key Cryptography
- 12:21Registration Authentication
- 14:21Hardware
- 15:28Hardware Enclave
- 16:36Protocols
- 19:41Hardware Authenticators
- 21:37Registration
- 23:27Gmail
- 25:45Directory
- 26:44Security
- 27:02Client Libraries
- 28:46Webauthn
- 29:47Browser API
- 41:49Lost Keys
related talks
 33mNavigating Passwordless Authentication with FIDO2 & WebAuthn
 29mWebAuthn and security keys - unlocking the key to authentication
 01h 14mWebAuthn: Theory and practice
 56mPasskeys 101: Technical Principles of FIDO
 33mSimple. Open. Mobile: A Look at the Future of Strong Authentication
 29mWhat the Authn? Passkeys Offer a Fresh Take to Authentication Dilemmas
 30mHow FIDO U2F Security Keys Work
 27mWebAuthn, Yubikeys, and You: What we wish we knew before...